In brief
On 1st and 2nd November, a wave of cyberattacks targeted refrigeration systems across the EU, prompting a joint emergency advisory from ENISA, the European Commission, Europol’s EC3, the EU CSIRTs Network and EU‑CyCLONe. The alert urges companies and manufacturers to comply with NIS2 and the EU Cyber Resilience Act, which mandates secure‑by‑design production and rapid incident reporting.
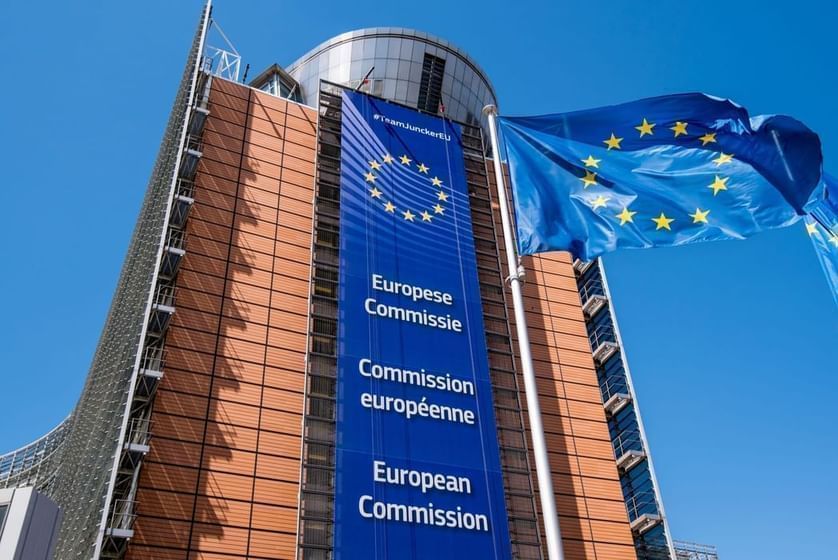
The European Union’s cybersecurity authorities issued an urgent advisory on 5 November, following a series of attacks on refrigeration systems that occurred on 1 and 2 November. The incidents, reported by several member states, prompted a coordinated warning from the European Union Agency for Cybersecurity (ENISA), the European Commission, Europol’s European Cybercrime Centre (EC3), the EU Computer Security Incident Response Teams Network (EU CSIRTs Network) and the European Cyber Crisis Liaison Organisation Network (EU‑CyCLONe). The alert advises organisations to reduce exposure to potential threats by immediately reviewing and strengthening their security measures.
Refrigeration systems, essential to food safety, pharmaceuticals, and industrial processes, have become a new target for cybercriminals. The rise in attacks suggests that attackers are exploiting vulnerabilities in the control software that governs temperature regulation and energy efficiency. The attacks occurred during a week when several large data centres and cold-chain facilities were subjected to remote intrusion attempts, illustrating that even legacy hardware is not immune to network-based exploits.
ENISA emphasized that the incidents are already being investigated by the national teams of the affected member states. The agencies are exchanging information and monitoring the situation through the EU CSIRTs Network. This collaboration enables quick dissemination of threat indicators and mitigation guidelines across the European Union.
NIS2 and the EU Cyber Resilience Act
The advisory stresses compliance with the Network and Information Security Directive, commonly referred to as NIS2. The directive requires organisations that provide essential services to implement robust risk management and to report significant incidents in a timely manner to national authorities or relevant computer security incident response teams. Compliance is mandatory for operators of food supply chains, where refrigeration systems are critical infra.
In addition to NIS2, the EU Cyber Resilience Act describes the responsibilities of hardware and software manufacturers. Since 11 September 2026, manufacturers must report severe incidents and exploited vulnerabilities through the Act’s Single Reporting Platform. On 11 December 2027, the Act’s core security requirements will go into effect, mandating secure‑by‑design and secure‑by‑default engineering for all connected IoT devices, including industrial refrigeration units. The Act also obliges manufacturers to devote security support throughout the product lifecycle and to patch vulnerabilities without delay.
"ENISA continues to promote secure‑by‑design and secure‑by‑default principles through technical advisories, guidance and information‑sharing initiatives, aiming to bolster cybersecurity across the EU," the agency said. The guidance includes step‑by‑step instructions for upgrading firmware, hardening network protocols, and aligning with the new EU compliance regime.
National cybersecurity response teams and crisis management authorities are actively monitoring progress and will continue to share updates. The EU organisations urge all stakeholders—from operators of cold‑chain logistics to manufacturers of industrial controllers—to act immediately. The measure aims to neutralise the evolving threat landscape and protect the integrity of essential services that rely on refrigeration technology.